
Remote work infrastructure: a step-by-step checklist
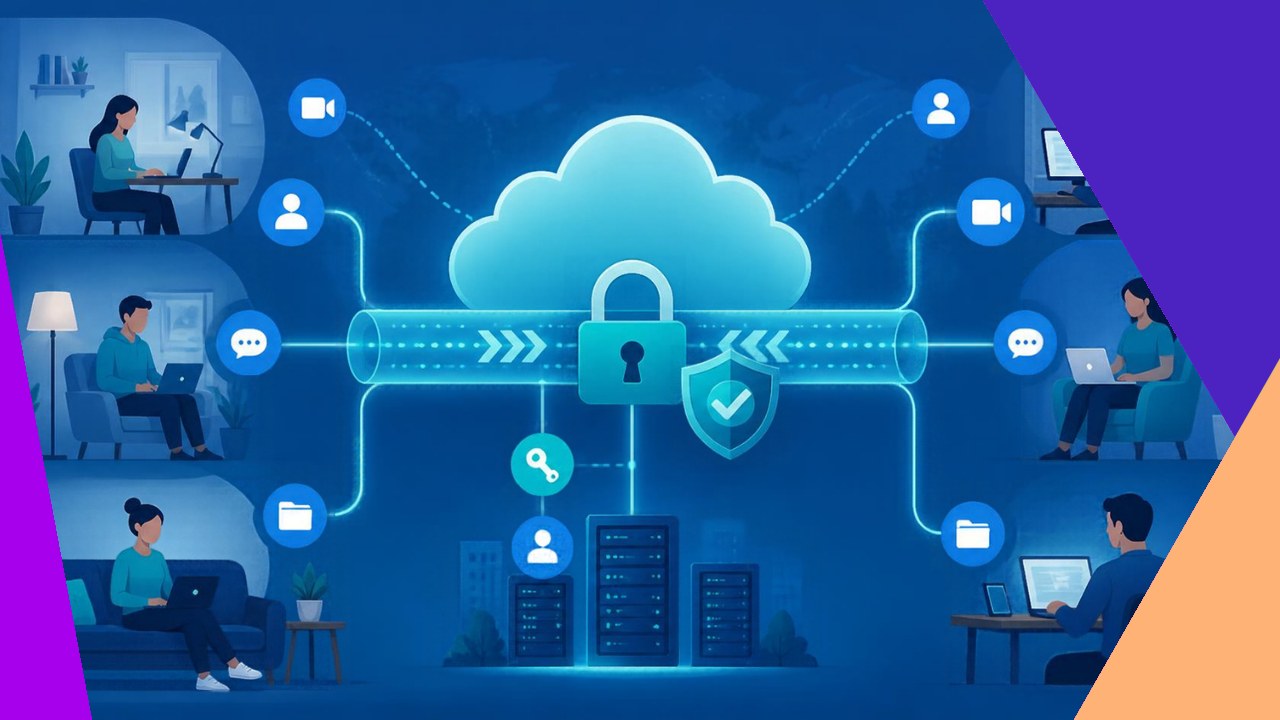
- Reliable remote work starts with the right technical backbone: managed devices, secure connections, cloud apps, and clear access rules.
- Work through the build in a set order, from endpoints to support, so each layer rests on a secure foundation.
- Security is not a final step. Bake it into every layer, from the laptop in someone’s kitchen to the identity that unlocks your systems.
Sending people home with a laptop is easy. Keeping them productive and safe once they are there is the hard part. That gap is where remote work infrastructure comes in: the devices, networks, apps, and controls that let a distributed team do real work without putting your data at risk.
Many companies grew their remote setups in a rush and never tidied them up. The result is a patchwork that mostly works, until a lost laptop or a shared password becomes a real problem. This checklist walks through the layers in the order to build them, so you get a setup that scales instead of a pile of tools to babysit.
The layers depend on each other, so work from the ground up. A secure app means little if the device opening it is already compromised.
The remote work infrastructure checklist
1. Inventory and standardize your devices
List every laptop, phone, and tablet that touches company data. You cannot protect what you cannot see.
Where you can, issue company-owned devices with a standard build, which keeps support simple and security consistent. If people use personal devices, set clear rules first. The NIST Guide to Enterprise Telework, Remote Access, and BYOD Security is a solid starting point for those policies.
2. Add endpoint management and protection
Loose devices are a liability. Enroll every one in a mobile device management tool so you can push updates, enforce disk encryption, and wipe a lost device remotely.
Add endpoint protection that watches for malware, and turn on automatic patching so machines stay current without anyone remembering to click “update.”
3. Secure the connection with VPN or zero trust
Home networks are not under your control, so the connection needs its own protection. A virtual private network (VPN) encrypts traffic between the worker and your systems, a familiar baseline for many teams.
A stronger model is zero trust, which checks every user and device instead of trusting them by default. As NIST puts it, zero trust grants “no implicit trust” based on network location. The Zero Trust Architecture guide (NIST SP 800-207) explains how to verify every request before it reaches a resource.
4. Move core apps and storage to the cloud
Office-bound servers rarely fit a remote team. Shift email, files, and business apps to cloud services people can open through a browser.
Keep company files in managed cloud storage, not scattered across personal drives. That gives you one place to set permissions, track versions, and recover deleted work, so a broken laptop never takes the only copy with it.
5. Standardize your collaboration tools
Pick a core set of tools for chat, video, and shared documents, then stick to it. Tool sprawl splinters conversations and leaves gaps attackers can slip through.
Match the stack to how your team works, and lean on the software that keeps distributed teams connected. Document which tool is for what, so nobody wonders where a decision was logged.
6. Centralize identity and access
Scattered logins are a weak spot. Route access through a single identity provider with single sign-on, so one secure account opens the tools each person needs. That also lets you cut off access the moment someone leaves.
Require multi-factor authentication everywhere it is offered, so a stolen password alone is never enough. Grant each role only the access it needs, and review those permissions on a schedule.
7. Set a security baseline across every layer
Tie the layers together with a baseline everyone follows. Encrypt data on devices and in transit. Keep backups you have actually tested by restoring from them. Write a short incident plan so people know who to call when something breaks.
Train the team too, because tools cannot fix a careless click. The CISA Telework Essentials Toolkit offers practical guidance for leaders, IT staff, and workers alike.
8. Build a remote support path
When something fails at home, people need help fast. Give them a clear way to reach IT, such as a help desk or ticketing tool, and give support staff remote access so they can fix issues without a desk visit.
Write short self-help guides for common problems, like resetting a password or reconnecting to the VPN. Many issues never reach a ticket when people can fix them in a minute.
How to roll it out without breaking things
Do not build all eight layers at once. Start with identity and devices, which carry the most risk, and pilot each change with a small group first. Review the whole stack at least twice a year. If your team is stretched, a managed services partner can run parts of this backbone for you.
Frequently asked questions
How much does remote work infrastructure cost?
Most costs are predictable monthly fees. Expect per-user charges for cloud apps, endpoint management, identity tools, and security software, with hardware as the main upfront expense. Budget per seat, so costs scale cleanly as you hire.
Is a VPN enough, or do we need zero trust?
A VPN is a fine starting point for smaller teams and a limited set of apps. Zero trust becomes worth the effort as you grow, add contractors, or move more work to the cloud. Many firms run both for a while, using the VPN for legacy systems while newer apps move to verified access.
What is the most common mistake companies make?
Treating security as an add-on rather than a design choice. Teams often buy tools fast and bolt on controls later, which leaves gaps. The fix is to decide your identity and access rules before the tools go live, then let those rules shape what you buy.
Can a small team manage this without a dedicated IT department?
Yes, within limits. Cloud platforms now bundle device management, identity, and security into packages a generalist can run. Once headcount or compliance demands grow, bring in a specialist or outsource the heavier pieces.






 Independent






