
How to choose a BPO when your industry has HIPAA, PCI-DSS, or FCA requirements
- Regulated-industry BPO selection requires evaluating compliance certifications as structural requirements, not vendor differentiators. A BPO without current certifications is disqualified before features or pricing enter the conversation.
- HIPAA, PCI-DSS, and FCA each create distinct obligations for BPO vendors: BAA execution for HIPAA, Attestation of Compliance for PCI-DSS, and data residency and audit rights documentation for FCA-regulated clients.
- The most common compliance failure mode in BPO outsourcing is selecting a vendor that claims compliance in marketing but cannot produce current documentation when requested before contracting.
- Afrishore BPO holds ISO 27001, ISO 9001, HIPAA, PCI-DSS, and GDPR certifications, operates in-office only (no work-from-home), and serves US, UK, Australian, and Canadian markets from a 30+ year track record.
Standard BPO vendor selection evaluates cost, scale, industry experience, and cultural fit. Regulated-industry BPO selection does all of that, but only after compliance documentation clears a baseline threshold.
In healthcare, financial services, insurance, and iGaming, a BPO partner that cannot demonstrate current regulatory certification is not a risk-adjusted option. It is a liability.
The challenge is that compliance claims are easy to make and difficult to verify without knowing what to ask for. Most vendor selection processes treat certifications as a checklist item: “do you have it?” and accept “yes” as sufficient.
The right process goes further: which version, what scope, when audited, and by whom.
For a foundation on what these frameworks require at the program level, see how HIPAA, PCI-DSS, and ISO standards interact in BPO environments.
This guide covers how to tell a genuinely compliant BPO partner from one that only sounds like it, before that difference gets expensive.
Why compliance-first BPO selection is different
In a non-regulated vendor selection, cost and capability lead the evaluation. Compliance is a hygiene factor confirmed near contract signature.
In a regulated-industry selection, that sequence inverts. A vendor that cannot produce current compliance documentation does not advance to capability or cost evaluation. The compliance gate is first, not last.
These distinctions are frequently misunderstood, and often misrepresented in vendor sales processes. They include the difference between SOC 2 Type I and Type II, a provider’s HIPAA business associate obligations, the scope of an ISO 27001 certification, and whether a vendor meets PCI DSS Level 1 rather than a lower merchant tier.
Knowing the difference before you enter a vendor selection process prevents the most common source of post-contract compliance surprises.
The practical consequence of selecting a non-compliant BPO vendor is not just a contract renegotiation.
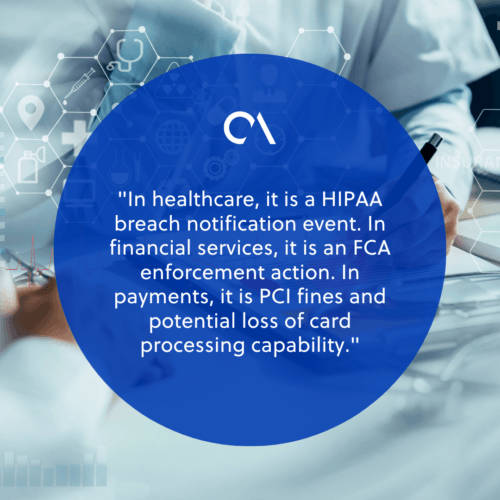
In healthcare, it is a HIPAA breach notification event. In financial services, it is an FCA enforcement action. In payments, it is PCI fines and potential loss of card processing capability.
The downside of getting this wrong is asymmetric.
Pro Tip: Build a compliance documentation request into the first stage of vendor evaluation, before RFP responses or capability presentations. Request the certification, the audit report, the scope document, and the date of the most recent assessment. Vendors that cannot produce these documents in the first round are not compliant BPO partners. They are vendors in the process of becoming compliant.
The three frameworks covered in this article have different evidentiary requirements. Understanding what each one demands before entering vendor conversations makes the evaluation faster and the outcome more reliable.
| HIPAA | PCI-DSS | FCA | |
|---|---|---|---|
| Core obligation | Business Associate Agreement (BAA) before any PHI access | Attestation of Compliance (AoC) from a Qualified Security Assessor | Contractual audit rights and data residency documentation |
| Key document to request | BAA template and PHI handling procedures | AoC, QSA identity, certified scope document | Data residency policy, BCP provisions, audit rights clause |
| Staff training requirement | Annual; all PHI-access personnel including QA staff | Annual; all cardholder data environment personnel | Background checks and role-specific vetting requirements |
| Consequence of non-compliance | HIPAA breach notification event; HHS OCR penalties | PCI fines; potential loss of card processing capability | FCA enforcement action; regulated firm remains liable |
| Produces a certification document? | No, BAA plus documented program | Yes, AoC from QSA | No, evidence-based, not certificate-based |
HIPAA: What to verify in a BPO
HIPAA (the Health Insurance Portability and Accountability Act) requires any vendor that handles protected health information on behalf of a covered entity to execute a Business Associate Agreement before any PHI is accessed or processed.
This is a non-negotiable legal requirement, not a contractual preference.
Beyond the BAA, HIPAA compliance in a BPO requires documented policies and procedures for PHI access, storage, transmission, and breach notification, and annual training for all personnel with PHI access.
For BPO operations, this means every agent, supervisor, and QA reviewer who touches client data in a healthcare context must be covered by the training program, not just the team leads.
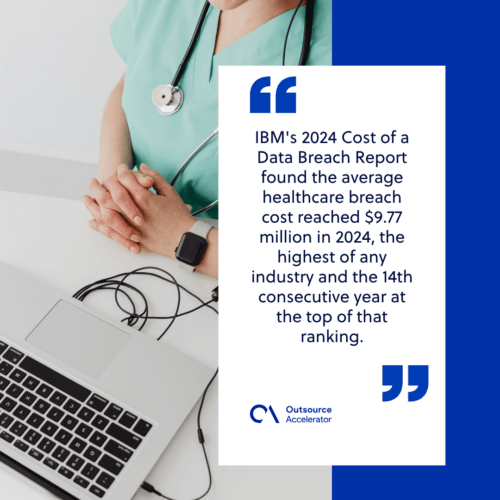
IBM’s 2024 Cost of a Data Breach Report found the average healthcare breach cost reached $9.77 million in 2024, the highest of any industry and the 14th consecutive year at the top of that ranking. For regulated healthcare operators, a BPO partner without verifiable HIPAA compliance is not a procurement decision. It is an exposure decision.
PCI-DSS: What to verify in a BPO
PCI-DSS (Payment Card Industry Data Security Standard) applies to any environment where cardholder data is stored, processed, or transmitted. BPOs handling payments on behalf of clients must maintain current PCI DSS certification appropriate to the transaction volume of the client programs they operate.
Key verification requirements for PCI-compliant BPO selection:
- Attestation of Compliance (AoC): the formal output of a PCI audit, confirming which systems and environments were assessed and when
- Qualified Security Assessor (QSA) identity: the firm that conducted the assessment. Third-party QSAs provide stronger assurance than self-assessment for higher merchant tiers
- Call recording architecture: under PCI DSS 4.0.1 (fully enforced April 2025), pause-and-resume recording is not acceptable for calls involving verbal cardholder data transmission
- Scope of certification: which specific sites, systems, and client programs are within the certified cardholder data environment
For more on PCI DSS call center requirements, see how PCI compliance frameworks apply to regulated-industry operations that buyers should verify before contracting.
FCA: What to verify in a BPO
The Financial Conduct Authority (FCA) is the UK’s financial services regulator, and its requirements extend to BPO vendors that handle FCA-regulated activity, data, or client communications on behalf of FCA-authorized firms.
Unlike HIPAA and PCI-DSS, FCA compliance for BPO vendors does not produce a single certification document. It requires demonstrable evidence that the vendor’s operations meet FCA expectations for outsourced financial services activities.
Key FCA-related requirements to verify in a BPO partner:
- Data residency documentation: where client data is stored and processed. FCA-regulated firms have strict requirements about cross-border data transfers
- Audit rights: the contract should explicitly grant the FCA-regulated client rights to audit the BPO’s compliance controls, including the right to conduct unannounced assessments
- Business continuity provisions: documented recovery time objectives and recovery point objectives for regulated business processes
- Staff vetting: background check and screening standards for agents handling financial services client data or regulated communications
Pro Tip: FCA-regulated firms are required under the FCA’s Senior Managers and Certification Regime (SM&CR) to remain responsible for outsourced activities. “We outsourced it” does not transfer regulatory responsibility. The due diligence your compliance team conducts on a BPO vendor before contracting is directly tied to your firm’s regulatory exposure if the vendor fails an FCA review.
How Afrishore BPO operates in regulated industries
Afrishore BPO provides outsourced customer service, back-office, and data operations for US, UK, Australian, and Canadian clients in regulated industries including iGaming, insurance, travel, and financial services.
Afrishore’s compliance posture is built around a documented multi-certification framework covering the major regulatory requirements of its client markets, with an in-office-only operating model that provides additional security controls compared to distributed home-based operations.
- ISO 27001 certified: information security management system certification covering data handling across all client delivery environments
- ISO 9001 certified: quality management system certification governing process consistency and service delivery standards
- HIPAA compliant: structured PHI handling protocols and BAA execution capability for healthcare-adjacent clients
- PCI-DSS certified: current certification for cardholder data environment operations within relevant merchant tiers
- GDPR compliant: documented data handling framework for UK and European client data requirements
- In-office only: all operations conducted in supervised, secured office environments with no work-from-home arrangements, providing physical access control not available in distributed staffing models
- 30+ years of operational history: parent company established in 1993, providing documented audit track record across compliance frameworks
Need a compliance-ready BPO partner for regulated work? Talk to the Afrishore team to scope your requirements.
Key takeaways
- Regulated-industry BPO selection begins with compliance documentation, not capability evaluation. A vendor without current certifications does not advance to the next stage.
- HIPAA requires a Business Associate Agreement and documented PHI handling; PCI-DSS requires an Attestation of Compliance with a specific scope; FCA requires audit rights, data residency documentation, and business continuity provisions.
- In-office operating models provide physical access controls for sensitive data environments that distributed home-based staffing models cannot replicate.
- Afrishore BPO holds ISO 27001, ISO 9001, HIPAA, PCI-DSS, and GDPR certifications, operates in-office only, and serves US, UK, Australian, and Canadian regulated-industry clients from a 30+ year operational track record.






 Independent






