A practical guide to remote work security best practices for IT teams
At a glance
- Remote work scatters your attack surface, so IT teams need security built for devices and people outside the office.
- Zero trust, multi-factor login, and secured devices do the heavy lifting against the biggest threats.
- Steady patching, encryption, and user training turn a risky remote setup into a resilient one.
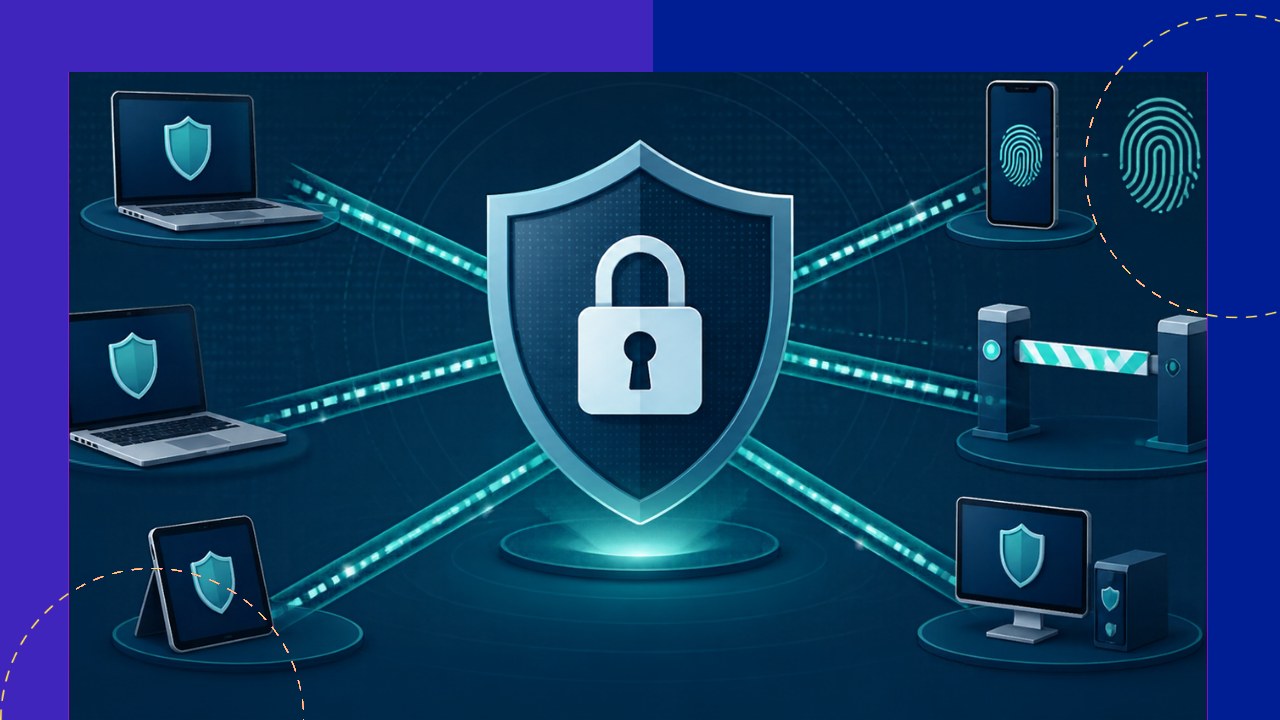
When everyone worked in one building, security had a clear perimeter. Remote work erased it. Solid remote work security best practices for IT teams rebuild that protection around users and devices wherever they are, so a laptop on a home network is as safe as one at a desk. Getting this right protects data, systems, and reputation at once.
Remote work security is the set of controls that keep distributed systems and data safe. For IT teams, it means securing many devices, networks, and logins they do not physically control.
Here are the practices that matter most.
Why remote work changes the game
Remote work multiplies the ways in. Home networks, personal devices, and public Wi-Fi all become doors an attacker might try.
The old idea of a trusted internal network no longer holds. Instead of guarding one perimeter, IT teams must protect every device and account on its own. That shift drives everything below.
Adopt a zero trust approach
Zero trust is the foundation of modern remote security. The National Institute of Standards and Technology explains that zero trust assumes there is no implicit trust granted to any account or device.
In practice, this means verifying every request, no matter where it comes from. Nothing is trusted just because it is inside the network. For remote teams, where there is no clear inside, this mindset fits perfectly.
Require multi-factor authentication
Passwords alone are weak, and remote work makes stolen credentials even more dangerous. Multi-factor authentication (MFA) adds a second check, such as a code or app approval.
Turn on MFA for every account that matters, especially email, admin tools, and anything cloud-based. It is one of the single most effective steps you can take, because it blocks most attacks that rely on a stolen password.
Secure every device
Each remote device is a potential entry point, so each needs protection. IT teams cannot assume a home laptop is safe.
Require up-to-date antivirus, disk encryption, and automatic locking on all work devices. Use endpoint tools, which manage and monitor devices from afar, to enforce these rules. Check device health before granting access, and keep personal and work use separate where you can.
Control remote access
How people connect matters as much as what they connect to. Open access invites trouble.
Use a virtual private network (VPN) or zero trust network access (ZTNA) to protect connections to company resources. Grant each person only the access they need for their role, and nothing more. Tight, least-privilege access limits the damage if one account is ever compromised.
Protect your data
Data is the real prize, so guard it directly. Encryption and backups are your safety net.
Encrypt data both in transit and at rest, so intercepted files are useless to an attacker. Back up important data regularly and test that you can restore it. If ransomware or a lost laptop strikes, good backups turn a disaster into an inconvenience.
Keep up basic cyber hygiene
Many breaches start with simple, avoidable mistakes. Consistent basics stop a surprising share of attacks.
The Cybersecurity and Infrastructure Security Agency lists using strong passwords, updating your software, and thinking before you click as core cyber hygiene. Patch systems promptly, since known flaws are a favorite target. Steady upkeep beats any single clever tool.
Train people and plan for incidents
Your people are both the biggest risk and the best defense. Remote staff face phishing and scams without a colleague to double-check with.
Train everyone to spot threats and report them quickly, and keep that training ongoing. Prepare an incident response plan too, so your team knows exactly what to do when something goes wrong. Speed and clarity in a crisis limit the harm.
Make security a shared habit
Tools only work when people use them well. The strongest remote security comes from habits, not just software.
Keep rules simple, explain why they matter, and make the secure path the easy one. Pairing these IT controls with everyday security habits for distributed teams closes the gaps that technology alone cannot. When security feels shared, people protect the company without being told twice.
Frequently asked questions
Is a VPN enough to secure remote work?
No. A VPN protects the connection, but it does nothing about weak passwords, unpatched devices, or phishing. It is one layer among many, which is why modern teams pair or replace it with zero trust access, MFA, and device controls.
What is the difference between a VPN and zero trust network access?
A traditional VPN often grants broad access to the network once a user connects, while zero trust network access grants access only to specific applications after verifying each request. ZTNA limits what a compromised account can reach, which makes it a stronger fit for remote work.
How can IT secure personal devices used for work?
Set clear policies, require security basics like encryption and updates, and use tools that separate work data from personal data. Where the risk is high, provide managed company devices instead, since that gives IT far more control over security.
What is the most common remote work security mistake?
Relying on passwords alone. Without MFA, a single stolen or reused password can open the door to company systems, so adding a second authentication factor is the fastest way to close the most common gap.
 Independent